The $100 Billion Shadow Cloud: How Crypto’s Decentralized GPU Networks Are Quietly Rewiring AI Infrastructure

Somewhere inside a data center in northern Virginia, a queue of AI inference jobs is waiting. Not for intelligence. Not for a breakthrough in model architecture. Just for a GPU — a physical chip that is, at this moment, already allocated to someone else, billed at $7.90 an hour, and almost certainly sitting at 40% utilization while the meter runs. This is the defining bottleneck of the AI era, and it is not a software problem. It is a hardware problem. And a growing coalition of crypto-native networks believes it has the answer.

Decentralized physical infrastructure networks — known in the industry as DePIN — have quietly been building a shadow cloud. One GPU at a time, one data center at a time, one blockchain transaction at a time. And in August 2026, the numbers are starting to demand attention.

The GPU Crisis Nobody Talks About Enough

The AI compute shortage is structural, not cyclical. SK Hynix and Micron have already sold out their entire 2026 high-bandwidth memory output. NVIDIA’s most advanced chips remain backordered across enterprise channels. Meanwhile, Amazon Web Services, Microsoft Azure, and Google Cloud collectively control roughly 65% of available data center GPU capacity — and they price that scarcity accordingly.

An NVIDIA H100 GPU costs approximately $7.90 per hour on legacy cloud platforms. For a startup training a mid-sized language model, that translates to tens of thousands of dollars before a single useful output emerges. For researchers at universities without deep-pocketed backers, the numbers are simply prohibitive. The broader market is feeling the squeeze: traditional cloud providers consume 50–70% of developer compute budgets, a figure that has climbed every year since 2022.

The decentralized compute sector was built for exactly this moment. And the sector’s growth rate — 265% in market capitalization over the past twelve months, from $5.2 billion to more than $19 billion — suggests that more than a few developers have noticed.

Who Is Actually Doing the Work

The DePIN compute landscape has consolidated around a handful of networks that have moved well beyond whitepaper ambitions into measurable, auditable production workloads.

Bittensor (TAO) remains the sector’s largest player by market capitalization at $2.12 billion. Its flagship inference subnet, Chutes, processes 425 billion tokens per day — a figure that places it among the most active inference networks on the planet, centralized or otherwise. The network generated $43 million in subnet revenue in Q1 2026 alone. Bittensor’s approach is unusual: rather than simply aggregating GPUs, it runs a competitive subnet economy where AI models compete for emissions based on performance benchmarks. The result is a self-improving marketplace of intelligence that no hyperscaler has replicated.

Akash Network (AKT) takes a more traditional cloud marketplace approach, built on the Cosmos blockchain and focused on general-purpose compute workloads. Its year-over-year usage growth of 428% heading into 2026 is one of the most striking adoption metrics in the sector. Monthly compute volume reached $3.36 million in Q3 2025, and the network has planned the acquisition of 7,200 NVIDIA GB200 GPUs to deepen its enterprise-grade capacity. Akash’s pricing advantage is its headline: H100 access runs $1.20 to $1.80 per hour — compared to AWS’s $4.50 to $5.50 for equivalent hardware, a 60–75% discount.

io.net (IO) claims access to more than 100,000 GPU devices across 130+ countries, positioning it as one of the largest aggregated compute pools outside the hyperscalers. Active developer addresses on the platform grew nearly fivefold — from 8,000 in Q1 2025 to more than 45,000 in Q1 2026. The network’s integration with Solana reduced transaction costs by approximately 99% compared to Ethereum, enabling the micro-payment architecture that makes sub-dollar GPU jobs economically viable. Enterprise platform Wondera documented $2.48 million in savings by running audio model training on 96 io.net GPUs rather than AWS infrastructure.

Render Network (RENDER) occupies a different niche — GPU rendering and AI model inference — and expanded its hardware base significantly in April 2026 by absorbing Salad Network’s roughly 60,000 GPUs. With a market cap above $2 billion and 600+ AI models onboarded to the platform, Render is increasingly the network of choice for creative AI workloads that require burst capacity without long-term commitment.

Aethir, though younger than the others, has delivered 1.4 billion compute hours with nearly $40 million in quarterly revenue — numbers that make it one of the fastest-growing compute networks in any category, decentralized or otherwise.

The Pricing Reality

The cost differential between decentralized and centralized compute is not marginal — it is transformative for a certain class of user. Across the DePIN sector, A100 and H100 GPU access runs 45–60% cheaper than AWS equivalents. Akash prices CPU workloads at 80–90% below AWS list prices. Hyperbolic, which serves more than 100,000 developers, advertises 75% cost savings compared to AWS, Azure, and Google Cloud through its orchestration layer.

These figures are not theoretical. AI image platform Leonardo.Ai reduced its inference costs by 50% while serving 19 million users by routing workloads through decentralized infrastructure. Academic researchers using decentralized frameworks documented 40–60% cost savings compared to university HPC cluster time in a 2024 study cited across the sector.

The broader market is paying attention. The DePIN compute sector generated an estimated $180–220 million in annualized protocol revenue as of Q1 2026, with verified on-chain revenue of $72 million annually across the top networks. The global decentralized compute market — currently valued at approximately $9 billion — is projected to reach $100 billion by 2032.

The Honest Limits

The sector’s advocates would be doing developers a disservice to ignore the genuine constraints that still separate DePIN from enterprise-grade cloud infrastructure.

Reliability variance is real. Decentralized networks aggregate hardware ranging from consumer gaming rigs to data center GPUs, and the quality gap between nodes is significant. Overprovisioning — allocating more resources than a job needs to guarantee completion — partially closes that gap, but it also erodes the cost advantage that makes DePIN attractive in the first place. A HashiCorp-Forrester report found that 94% of organizations already overspend on cloud infrastructure, with 59% citing overprovisioning as the primary cause.

Service-level agreement enforcement is another genuine gap. Cryptographic slashing penalties — where node operators lose staked tokens for failing to deliver — are not the same as the legally binding uptime guarantees that enterprise procurement teams require. The decentralized networks lack, as one analysis put it, “the legal and technical frameworks to enforce binding, enterprise-grade SLAs.”

And then there is the token accounting problem. Each token transfer constitutes a taxable event in many jurisdictions. Corporate finance departments accustomed to a single AWS invoice face a genuinely complex compliance challenge when paying for GPU time in IO or AKT. Accounting software has not caught up.

Frontier model training — the kind that requires tens of thousands of GPUs running in tight synchrony for weeks — remains firmly in the hyperscaler’s domain. The microsecond-level coordination required simply cannot be achieved across geographically dispersed anonymous nodes. DePIN’s sweet spot is inference workloads, batch processing, and short-duration training runs, which together represent up to 70% of global GPU demand. That is not a narrow market.

What the Convergence Actually Looks Like

The most sophisticated players in the enterprise AI space are not making an either/or choice between hyperscalers and decentralized compute. They are building hybrid architectures: centralized clouds for proprietary data storage and long-duration training, and decentralized networks for burst inference capacity where cost is the primary variable.

This is, in retrospect, the obvious outcome. AWS and Azure have structural advantages in training that will not disappear. But the inference market — where a deployed model responds to millions of user queries every day — is exactly the workload that decentralized networks are optimized to handle cheaply and at scale.

Gensyn, backed by Andreessen Horowitz with a $43 million Series A, is building verification infrastructure that addresses one of DePIN’s core technical challenges: how do you prove that a remote node actually performed the computation it claims? Its Verde Verification Protocol uses refereed delegation to provide cryptographic proof of work without trusting the node operator. If that problem is solved at scale, the enterprise adoption barrier drops significantly.

The sector’s most clear-eyed observer framed it simply: scale arrives “when developers pay with credit cards, SLAs look familiar, and blockchain mechanics stay invisible in the background.” That moment has not arrived yet. But the infrastructure being built today is, piece by piece, designed to make it inevitable.

What This Means for You

If you are a developer building AI applications, the decentralized compute sector deserves a line item in your infrastructure budget today — not as a bet on the future, but as a practical cost-reduction tool for inference workloads. The 45–75% savings figures are real, documented, and achievable for the right class of job. Start with batch inference. Route overflow capacity to Akash or io.net. Measure the actual savings before committing further.

If you are an investor, the DePIN compute sector’s 265% growth in market cap over twelve months represents momentum — but the valuations of the largest networks already reflect significant optimism about enterprise adoption timelines that remain uncertain. The more interesting risk-reward may lie in the verification and orchestration layer: the infrastructure that makes decentralized compute trustworthy enough for enterprise buyers is where the next wave of value creation is likely to concentrate.

If you are simply watching the AI infrastructure story unfold, keep your eye on the pricing gap. As hyperscalers respond to DePIN competition by reducing on-demand GPU pricing — a dynamic already beginning to emerge — the sector’s cost advantage will narrow. The networks that survive that compression will be the ones that offer something AWS cannot: genuine decentralization, censorship resistance, and the ability to deploy AI infrastructure in jurisdictions where hyperscaler data centers do not exist.

The cloud that Silicon Valley built is fast, reliable, and expensive. The shadow cloud that crypto is building is cheaper, scrappier, and catching up faster than anyone in Virginia expected.


Sources:

Congress Missed the Window. Now the SEC Is Writing the Rules Without It.

For three years, the crypto industry has been promised a law. A real one — not enforcement actions and no-action letters, not ambiguous agency guidance and courtroom settlements, but actual legislation passed by Congress and signed by the president. The Digital Asset Market Clarity Act came closer than anything before it. It passed the House with a bipartisan 294-134 majority in July 2025. It cleared the Senate Banking Committee in May 2026 by 15-9. And then, in the final days before the August recess, it ran out of time — no floor vote, no final passage, no law. Just another deadline missed on Capitol Hill.

The SEC, watching from across town, apparently decided it had waited long enough.

On August 18, 2026 — ten days after the Senate went home empty-handed — the Securities and Exchange Commission proposed “Regulation Crypto Assets,” the most ambitious bespoke crypto rulemaking in the agency’s history. It didn’t ask Congress for permission. It didn’t wait for the CLARITY Act to get reconciled, debated, or finally voted on. It moved. And in doing so, it may have fundamentally changed how American crypto regulation unfolds for the next decade.


The CLARITY Act: How a 294-Vote Win Became a Senate Standoff

The Digital Asset Market Clarity Act — known in Washington as H.R. 3633 — is a 309-page framework designed to answer the most fundamental question in American crypto: who regulates what? For years, the SEC and CFTC have operated in an uneasy, overlapping gray zone, each claiming jurisdiction over different corners of the same industry. Bitcoin is clearly a commodity. Ether, after years of back-and-forth, landed in similar territory. But the thousands of tokens in between — the DeFi protocols, the gaming assets, the layer-2 governance coins — exist in genuine regulatory limbo, subject to whichever agency decides to act first.

The CLARITY Act proposed to fix that. It would create a new legal category — the “digital commodity” — covering tokens operating on sufficiently decentralized, functioning blockchains, with the CFTC as their primary regulator. Investment contracts, those tokens tied to promises of future profits from others’ efforts, would remain under SEC jurisdiction. Critically, the bill creates a maturity certification process that would allow a token to migrate from SEC-regulated security status to CFTC-regulated commodity status once a project proves its network is decentralized enough that no single team controls the outcome.

For an industry built on tokens that launch as securities and grow into infrastructure, this pathway was the entire point. Exchanges would register with the CFTC rather than navigating dual oversight. Self-custody wallets would receive explicit legal protection. And customers would get bankruptcy priority protections — a direct response to the FTX collapse, where customer assets became general creditor claims in a courtroom free-for-all.

The bill cleared the Senate Banking Committee on May 14, 2026, by a 15-9 vote — a genuine bipartisan majority in a year when genuine bipartisan anything is remarkable. The revised Senate text was published and placed on the Senate Legislative Calendar on June 1. A cloture motion was filed August 8. And then Congress went on recess. A procedural vote is now scheduled for September 15, 2026, but the same fault lines that cost the bill its August window remain unresolved: Democratic senators are demanding conflict-of-interest protections around presidential crypto holdings; banking lobbyists are fighting provisions that would let crypto platforms offer interest-bearing stablecoins; and DeFi advocates are pushing back on anti-money-laundering requirements they argue would criminalize open-source code.

If September slips, most observers expect the bill to carry over into 2027 — at which point it would need to restart its Senate path from the beginning.


The SEC’s Answer: Regulation Crypto Assets, Explained

Into this vacuum stepped Chairman Paul Atkins, who has made “Project Crypto” the defining initiative of his tenure at the SEC. The proposed Regulation Crypto Assets, published August 18, is the centerpiece — a framework that doesn’t wait for Congress to define what a digital asset is before offering a pathway for token projects to raise capital legally in the United States.

The core structure operates on two exemptions from the standard securities registration process. Think of it as a ladder based on how much money a project wants to raise:

Tier 1 — The Startup Exemption

Projects raising up to $5 million over four years qualify for the startup exemption. There are no audited financial statements required — just principles-based narrative disclosures that explain to investors what the project does, who runs it, and what the token is supposed to be used for. The exemption is available once per crypto asset, can be used by non-U.S. entities, and crucially, places no resale restrictions on the tokens sold. That last point is significant: under current law, tokens sold in most private offerings are locked up for months or years, killing liquidity and limiting retail participation. Regulation Crypto Assets proposes to change that at the earliest stage of a project’s life.

Tier 2 — The Fundraising Exemption

Larger projects face more requirements. Tier 2A allows raises of up to $20 million annually with no assurance requirement on financial statements. Tier 2B allows up to $75 million annually, but requires audited financials and SEC staff review of an offering statement before the raise can begin. Both Tier 2 options require the issuer to be a U.S. entity with U.S.-based management and assets — a deliberate effort to encourage projects to stay onshore rather than incorporating in the Cayman Islands or Singapore to escape American regulation.

Both exemptions also override state securities laws for secondary market transactions — meaning a token sold under Regulation Crypto Assets can trade across state lines without triggering a patchwork of fifty different regulatory regimes.


The Exit Ramp That Changes Everything

If the two-tier exemption structure is the headline, the safe harbor provision buried inside Regulation Crypto Assets may be the more consequential long-term development. Under the proposal, once a project completes the “essential managerial efforts” it promised investors — once the team has built the thing it said it would build and the network runs without them — the investment contract ceases to exist. The crypto asset exits securities regulation entirely.

This is not a minor procedural footnote. For years, the SEC’s enforcement position has been that once a token is issued as a security, it remains a security in perpetuity — regardless of how decentralized the underlying network becomes. That position made launching in America an existential risk: build a successful, genuinely decentralized protocol and you might still face an enforcement action for the ICO you ran five years ago. The proposed safe harbor directly repudiates that logic. It creates, for the first time, a clear legal exit ramp from securities treatment based on demonstrated network maturity.

It is, in miniature, exactly what the CLARITY Act’s maturity certification process was designed to achieve through legislation. The SEC got there through rulemaking instead.


Two Tracks, One Destination — But Different Risks

The parallel development of the CLARITY Act and Regulation Crypto Assets has created an unusual dynamic in Washington: two legitimate pathways to crypto regulatory clarity moving at very different speeds. The SEC’s rulemaking is faster — it doesn’t require 60 Senate votes, presidential signature, or resolution of contested ethics provisions. But it carries its own vulnerability. Regulatory rules can be challenged in court. They can be reversed by a future administration. They can be narrowed by subsequent agency guidance. Legislation, once passed, is dramatically harder to undo.

The SEC and CFTC have already moved in tandem on at least one major pre-legislative step: in March 2026, the agencies jointly classified 16 crypto assets as digital commodities — effectively front-running Congress on the most contested jurisdictional question in digital asset regulation. That joint classification gave clarity to the market but created its own legal uncertainty, as the agencies acted without explicit statutory authority to do so.

Industry groups are now watching both tracks carefully. The Blockchain Association’s letter of support — signed by 160 former law enforcement officials in June 2026 — reflects the industry’s preference for the legislative route. But as the September 15 procedural vote approaches, few insiders are willing to bet that the CLARITY Act will pass before year-end. The safer money, increasingly, is on Regulation Crypto Assets becoming the operative framework for U.S. token offerings in 2027.


What This Means for You

If you hold crypto, none of these regulatory developments change how your existing holdings are taxed or traded. What they do change is the environment in which the next generation of crypto projects will launch — and that has downstream effects on every investor.

  • If you invest in early-stage token projects: Regulation Crypto Assets, once finalized, could dramatically expand the number of legally compliant token sales available to U.S. retail investors. Today, most early rounds are restricted to accredited investors. The startup exemption’s removal of resale restrictions could change that.
  • If you use DeFi protocols: The CLARITY Act’s DeFi protections — and its self-custody wallet provisions — remain the strongest legal shield for non-custodial users. The SEC’s rulemaking doesn’t directly address DeFi. How the September Senate vote plays out matters more for DeFi users than for token investors.
  • If you hold assets on centralized exchanges: The CLARITY Act’s bankruptcy priority provisions are the most direct protection for exchange customers. Until that law passes, the legal status of your exchange-held assets in a platform collapse remains uncomfortably similar to what FTX customers faced.
  • If you’re building in crypto: The 60-day comment period on Regulation Crypto Assets runs through mid-October. If you have a token project, this is the moment to engage — the final rule will be shaped by what the SEC hears during that window.

The Clock Is Running

When the Senate went home in August without passing the CLARITY Act, it left the cryptocurrency industry in the same legal limbo it has occupied for a decade. But the SEC’s response — moving swiftly with a comprehensive rulemaking framework of its own — suggests that the era of crypto operating in genuine regulatory uncertainty may finally be ending, even if the mechanism for ending it isn’t the one the industry expected.

The September 15 procedural vote will tell us whether Congress can find 60 votes to advance the bill it has spent two years negotiating. If it can, the CLARITY Act remains the stronger, more durable framework — a legislative foundation that no future SEC chair can reverse with a stroke of a pen. If it can’t, Regulation Crypto Assets becomes the de facto law of the land for American token offerings, reshaping how projects raise capital, how tokens trade, and how projects eventually exit securities regulation altogether.

Either way, the window for inaction has closed. America’s crypto rulebook is being written right now — in committee rooms, in agency press releases, and in a 60-day comment period that most retail investors don’t know is happening. The outcome will define the next decade of digital asset markets. Whether Congress gets to the finish line first, or whether the SEC beats it there, is the only question left.


Sources:
CLARITY Act 2026 Status: Where Crypto Regulation Stands — Tech Insider
SEC Proposes New Regulation Crypto Assets — SEC.gov
The Wait Is Over: SEC Proposes Regulation Crypto Assets — Sidley Austin LLP
US Crypto Policy Tracker: Legislative Developments — Latham & Watkins
SEC and CFTC Joint Interpretation on Crypto Asset Regulation — Norton Rose Fulbright

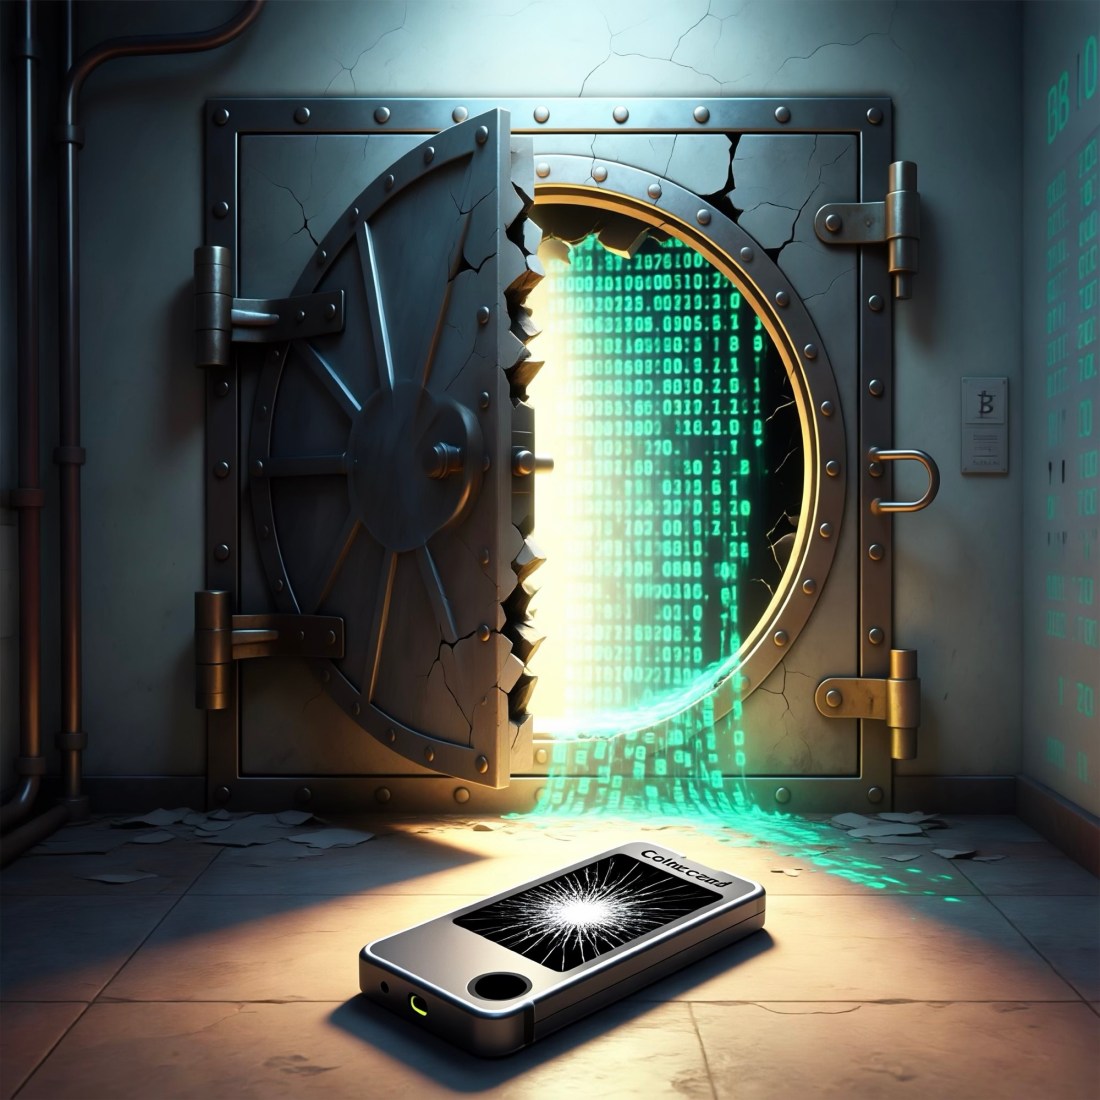
The Hardware Vault That Wasn’t: Inside the $130 Million Coldcard Hack That Shook Bitcoin Self-Custody

Jonathan Goodman did everything right. He never shared his seed phrase. His Coldcard devices never touched the internet. He kept them in a safe. And on the morning of July 30, 2026, he watched $1.6 million in Bitcoin drain from his wallet in minutes — without a single keystroke from anyone who knew his password.

Goodman’s story is not an anomaly. It is the opening chapter of what security researchers are calling the most consequential hardware wallet exploit in crypto history — a firmware flaw baked into Coldcard devices since March 2021 that has quietly exposed the private keys of thousands of users to brute-force attack. By late August 2026, on-chain investigators had tied the vulnerability to more than $130 million in stolen Bitcoin, with at least a dozen separate hacker groups still actively scanning for victims.

For a community that has long held hardware wallets as the gold standard of self-custody, the Coldcard incident is a seismic event — one that demands both immediate action and a hard rethink of what “secure” really means in 2026.


How a Single Firmware Bug Cracked Open Thousands of Wallets

The root cause traces back to firmware version 4.0.1, released by Coinkite in March 2021. According to blockchain intelligence firm TRM Labs, which conducted a forensic analysis of the exploit, a bug in the random number generation code caused affected devices to use weak software-based randomness instead of the hardware entropy the device was designed to rely on.

The practical consequence was devastating: instead of producing a seed phrase backed by 128 bits of true randomness — a number so astronomically large that brute-forcing it would take longer than the age of the universe — the flawed firmware generated seeds with an effective entropy as low as 40 bits. At modern computing speeds, that keyspace can be exhausted systematically.

In plain terms: an attacker who knows a wallet was generated on a vulnerable Coldcard doesn’t need to steal your device, intercept your seed phrase, or trick you into clicking a phishing link. They can simply reconstruct your private key from scratch using publicly visible Bitcoin addresses. The wallet that was supposed to be your fortress became, in effect, a combination lock whose combination could be guessed.


Five Years of Exposure: A Timeline Nobody Was Tracking

What makes the Coldcard breach particularly sobering is its age. The vulnerable firmware shipped in March 2021. Anyone who set up a Coldcard wallet — and generated a new seed phrase on that device — between that date and a patch released in August 2026 may have been exposed for more than five years without knowing it.

The first wave of confirmed thefts hit on July 30, 2026, when roughly 594 BTC disappeared from 25 wallets in under 25 minutes. Three additional waves followed between August 1 and August 4. Coinkite published an initial security advisory on August 1 and updated it on August 3; a comprehensive firmware patch was not released until August 20, 2026.

The affected device models and firmware ranges, per Coinkite’s official disclosure:

  • Mk2 / Mk3: Firmware versions 4.0.1 through 4.1.9 (analysis by Block suggests 4.0.0 may also be vulnerable)
  • Mk4 / Mk5: Standard firmware before 5.6.0; Edge firmware before 6.6.0X
  • Coldcard Q: Standard firmware before 1.5.0Q; Edge firmware before 6.6.0QX

Total affected addresses: over 5,200, according to TRM Labs tracking. The stolen sum, pegged at roughly 1,816 BTC, fluctuated between $112 million and $130 million depending on Bitcoin’s price at the time of each wave. Tom Robinson, co-founder of blockchain analytics firm Elliptic, confirmed the upper figure is “roughly correct.”


Not One Thief — At Least a Dozen

One of the more unsettling dimensions of this story is its scale of perpetrators. Galaxy Research, which has been monitoring on-chain activity linked to the exploit, identified at least a dozen different hacker groups targeting Coldcard users in parallel — suggesting that knowledge of the vulnerability spread through criminal networks before any public disclosure.

This pattern — where a zero-day circulates privately in exploit markets while the affected vendor remains unaware — is increasingly common in crypto security. What is less common is a flaw of this magnitude surviving for five-plus years in widely-used consumer hardware. The Coldcard MK3, the device most prominently associated with the early theft waves, has long been marketed to serious Bitcoin holders who prioritize security above all else. Many victims were precisely the users who thought they were best protected.

The Coinsbuy exchange breach in July 2026, which drained $8 million, and wider July losses of over $242 million across the industry, underscored a broader trend that the Coldcard incident crystallized: in 2026, most major crypto losses are no longer coming from smart contract exploits. They are coming from compromised keys — whether through phishing, supply-chain attacks, or, as here, cryptographic weaknesses in the device meant to protect them.


The Self-Custody Debate Cracks Wide Open

Bitcoin’s core value proposition has always included the ability for individuals to be their own bank — to hold assets without reliance on any third party. Hardware wallets like Coldcard were the technology that made that proposition practical for serious holders. The exploit has triggered a pointed reassessment of that promise.

Lorenzo Valente of ARK Invest offered a frank assessment: users who chose self-custody have “traded counterparty risk for software risk, hardware risk, supply-chain risk” and may be “better off holding funds across several exchanges or ETFs.” David Lawrence, co-founder of Amicus, predicts that new investors will increasingly favor regulated custodial products like BlackRock’s iShares Bitcoin Trust (IBIT) as a result of the breach, suggesting “that dream is over” for widespread personal cold storage adoption.

Not everyone agrees. Nick Neuman, CEO of multi-signature custody firm Casa, acknowledged the difficulty of expecting everyday users to manage complex entropy inputs — calling Coinkite’s new requirement to manually generate randomness through 65 key presses, 50 dice rolls, or 128 coin flips “a non-starter for 99% of people” — but argued the answer is better tooling and multi-signature setups, not a return to exchange custody. Taproot developer Udi Wertheimer struck a harder note: the idea of Bitcoin “resting easy” in cold storage while ignoring the security of the underlying device “is currently unrealistic.”


What Coldcard Users Must Do Right Now

If you own a Coldcard device, the following steps are not optional. Coinkite CEO NVK made the urgency explicit in his public advisory: “If you generated a seed using a Coldcard wallet, move your funds now.” Critically, updating firmware alone does not protect an already-compromised seed. The seed must be regenerated from scratch on patched hardware, and all funds migrated to the new wallet.

  1. Do not update firmware and assume you are safe. An existing seed generated during the vulnerable window remains crackable regardless of your current firmware version. Updating first, then migrating, is safer than migrating on unpatched firmware — but the migration is the essential step.
  2. Install the patched firmware for your model: version 5.6.1 for Mk4/Mk5, version 1.5.1Q for the Coldcard Q. Mk2/Mk3 users should refer to Coinkite’s official advisory for their specific patch.
  3. Generate an entirely new seed phrase on the updated device. Coinkite now requires physical entropy input — at minimum 65 key presses, 50 rolls of a standard six-sided die, or 128 coin flips — to ensure the new seed cannot be compromised by the same class of bug.
  4. Do not restore or clone your old wallet. Migrating by importing the original seed into a new wallet defeats the purpose entirely. Start fresh.
  5. Move all funds from old addresses to your new wallet immediately after setup. Every hour of delay is an hour those funds remain at risk.
  6. Monitor Coinkite’s official advisory page for updates. The scope of affected devices and firmware versions may expand as forensic analysis continues.

What This Means for You — Even If You Don’t Own a Coldcard

The Coldcard exploit carries a lesson that extends well beyond any single product or brand. Hardware security devices are not magical objects — they are software running on physical chips, and software has bugs. The confidence that many holders place in their cold storage devices may not be fully warranted, and the incident highlights three principles that every serious crypto user should internalize.

Firmware matters as much as hardware. The physical security of a Coldcard is real — but the cryptography that protects your seed is implemented in code. Keep devices updated, monitor manufacturer security advisories, and treat a security patch with the same urgency you would a bank fraud alert.

Diversification applies to custody, too. Concentrating all holdings behind a single key generated by a single device creates a single point of failure. Multi-signature setups — where spending requires approval from multiple independent keys on different hardware — would have limited the blast radius of this exploit significantly.

Verify, don’t trust. Coinkite’s new entropy requirements are inconvenient by design. True randomness cannot be assumed; it must be generated and verified. If your security model relies on a device silently doing the right thing, you are trusting a black box — and black boxes break.


Jonathan Goodman kept his devices in safes. He did everything the guides told him to do. The lesson from his $1.6 million loss is not that self-custody is dead — it is that security is a practice, not a product. Hardware wallets remain one of the strongest tools available, but they require active oversight, regular firmware hygiene, and a sober understanding of what they can and cannot protect against. The Coldcard breach is a brutal reminder that in crypto, the lock on your vault is only as strong as the math it runs on.


Sources:
TRM Labs — The Largest Hardware Wallet Exploit of 2026: Inside the $116M Coldcard Hack
TechCrunch — Hackers steal over $130M by exploiting bug in offline hardware wallets
CoinDesk — Coldcard Exploit Shakes Faith in Self-Custody, May Push Investors to ETFs
Fortune — Bitcoin owners rocked by $116 million hack: What we know about the Coldcard exploit
Cryptonomist — Coldcard Seed Vulnerability Exposes Crypto Wallets to Risk
CoinMonks — July 2026 Crypto Hacks: $242M+ Lost

Nobody Cracked the Code: How Crypto Hackers Bypassed Security in 2026

Nobody cracked the code. Nobody reverse-engineered a smart contract in a dark room for weeks. On August 23, 2026, an attacker walked into Term Labs’ decentralized lending vaults and walked out with $8.5 million by doing something almost mundane: they bought enough votes to simply ask for the money.

That is not a metaphor. The attacker accumulated governance tokens until they controlled 100% of the voting power in four of Term Finance’s strategy vaults and roughly 91% of its Ethereum Meta Vault. Then they passed a proposal instructing those vaults to transfer 2,843 ETH and 1.68 million USDC directly to an address they controlled. No exploit. No buffer overflow. No flash loan. Just governance — the same democratic mechanism protocols use to let their communities steer decisions — turned into a weapon.

The Term Labs incident is the sharpest recent example of a shift that has been building all year: crypto security threats in 2026 are no longer primarily about finding bugs in code. They are about exploiting the humans, the institutions, and the social systems that surround that code. And by every measurable standard, those attacks are accelerating.

A Year That Has Already Broken Records

Through the first five months of 2026, more than $840 million in cryptocurrency was stolen across 50-plus documented incidents — a 70 percent increase over the same period in 2025, according to analysis by AltFins. The research firm CCN put the figure even higher, counting more than $1 billion in losses across 22 major exploits before June arrived.

April 2026 was the worst single month in the history of DeFi theft, with approximately $630 million drained across multiple attacks. The two largest — a $292 million compromise of KelpDAO’s bridge infrastructure and a $285 million governance manipulation targeting Drift Protocol — happened within weeks of each other, and together they represent the clearest signal yet that attackers have moved up the stack from code vulnerabilities to systemic design failures.

Chainalysis, which tracks stolen crypto flows, has attributed roughly 76 percent of all crypto hack losses in 2026 to a single threat actor: Lazarus Group, the North Korean state-sponsored hacking organization. That figure should give pause. The most dangerous force in cryptocurrency security is not a rogue teenager in a hoodie — it is a nation-state with a decade of experience draining blockchain protocols to fund a weapons program.

The Attack Vector Has Shifted Upward

For most of DeFi’s short history, the dominant security risk was code. A reentrancy bug, an integer overflow, a missing validation check — these were the vulnerabilities that handed attackers hundreds of millions of dollars and kept smart contract auditors employed. That era is not over, but it is no longer the primary threat.

AltFins’ breakdown of 2026 attack vectors tells a striking story. Key and credential theft — stealing the private keys or admin access that control protocols rather than exploiting the protocols themselves — accounts for 72 percent of losses. Bridge and infrastructure compromises account for another 18 percent. Traditional smart contract logic flaws have fallen to just 8 percent of total losses.

The KelpDAO attack illustrates why bridges are such attractive targets. Cross-chain bridges now hold an estimated $21.94 billion in total value locked. They are, by architectural necessity, complex and multi-party systems — exactly the kind of infrastructure where a single point of compromise can cascade into a nine-figure loss. Since 2022, bridges have generated $2.8 billion in cumulative losses, accounting for roughly 40 percent of all Web3 hack proceeds.

The Term Labs governance exploit represents the next evolutionary step. The attacker’s initial capital was just 2 ETH — approximately $4,800 — sourced through Tornado Cash to obscure the trail, according to security firm PeckShield. That seed funded a snowballing accumulation of governance tokens that eventually gave the attacker absolute voting control. The vaults were built on Yearn v3 contracts, and Term Labs was careful to note that its core lending architecture remained unaffected. But the damage was done: $8.5 million gone, the protocol’s reputation shaken, and the broader DeFi community left asking an uncomfortable question — if governance can be bought cheaply enough, what exactly is the difference between a decentralized protocol and a protocol waiting to be controlled?

When the Attack Is Your Personal Data

Not every security incident in August 2026 involved direct theft of crypto. On August 17, hardware wallet manufacturer SafePal disclosed a data breach affecting 39,798 customers — a breach that had gone undetected for more than thirteen months, spanning from March 2, 2025 through April 11, 2026.

The vulnerability was almost embarrassingly simple: an authorization flaw in an order-tracking plugin that allowed anyone to view another customer’s purchase receipt and delivery details by changing a single number in the URL. No funds were directly stolen. No seed phrases, private keys, or payment credentials were exposed. But the breach handed attackers a detailed list of names, home addresses, and order histories for nearly 40,000 people who had paid money for hardware designed to keep their crypto safe.

SafePal patched the flaw immediately upon discovery, removed more than 30 fraudulent phishing websites spun up in the breach’s wake, and commissioned a third-party security audit. Going forward, the company announced it would retain customer data for only 90 days after an order is fulfilled. But the warning issued to affected customers is the thing that matters most: those users now face “heightened phishing and impersonation risks.” Anyone who received a hardware wallet at a known address and whose name sits in a leaked database is a target for social engineering attacks for years to come.

The Threat No Password Can Stop

The most disturbing security trend of 2026 cannot be solved with a firmware update or a hardware upgrade. Chainalysis documented a surge in what security researchers call “wrench attacks” — physical, often violent crimes in which attackers force crypto holders to transfer funds at gunpoint, through kidnapping, or by threatening family members.

Through the first half of 2026, approximately $30 million was stolen through violent crypto theft — a number on pace to approach the record $58 million stolen across all of 2025. France has become the epicenter of the trend, with more than 70 documented incidents by mid-year according to French authorities, compared to fewer than one per month before 2025. The victims are not tourists flashing hardware wallets in public: 93 percent of French victims are local residents, targeted specifically because their names and addresses appear in leaked databases.

Kidnappings now account for 52 percent of violent crypto theft incidents in 2026. Home invasions account for another 37 percent. And in a development that marks a significant escalation, 25 to 30 percent of victims globally — and 40 percent in France — are not crypto holders themselves but family members and associates of people known to hold significant crypto wealth. The attackers, in other words, are adapting. When the primary target has good physical security, they go after someone who does not.

The root of France’s epidemic appears to trace back to a 2024 breach of tax authority records, in which a government official allegedly stole and sold dossiers on high-net-worth crypto holders including names, addresses, holdings, and phone numbers. That breach did not make headlines at the time. The physical attacks it enabled have been making headlines ever since.

What This Means for You

The cumulative picture of crypto security in 2026 is one of a threat landscape that has matured faster than most holders’ mental models of the risk. The dangers are no longer limited to clicking a bad link or connecting to a malicious dApp. They include the governance structures of protocols you lend to, the data retention policies of companies whose hardware sits in your drawer, and — in the most extreme cases — your physical safety and that of people who know you hold crypto.

That requires a different kind of response than most security guides offer. A few concrete principles have become more important than ever:

  • Treat DeFi governance as a security variable. Before depositing into any protocol, examine how its governance works, how concentrated voting power is, and what a malicious governance proposal could do to your funds. The Term Labs attack was preventable — protocols with timelocks, multi-sig requirements for large withdrawals, and decentralized governance token distribution are meaningfully harder to compromise this way.
  • Assume your address is known. Between exchange KYC breaches, hardware wallet company databases, and on-chain analytics, the assumption that your crypto holdings are private is almost certainly wrong. Act accordingly: be skeptical of unsolicited contact, verify through official channels before taking any action, and understand that the SafePal breach timeline (13 months undetected) means a company can be compromised long before you hear about it.
  • Discretion is a security measure. Chainalysis makes the point bluntly: do not publicly disclose your crypto holdings. This applies to social media, professional networking profiles, and casual conversation. The Chainalysis data shows that the vast majority of violent crypto theft victims are local residents targeted because their holdings were known or discoverable — not random victims of opportunity.
  • Review your DeFi exposure for bridge risk. Any asset sitting in a cross-chain bridge, a protocol that relies on bridge infrastructure, or a multi-chain yield strategy carries elevated risk. The $2.8 billion in cumulative bridge losses since 2022 is not a statistical anomaly — it reflects a structural weakness in how cross-chain liquidity is managed.

The Security Gap Is Widening

There is a pattern visible in the 2026 security data that should concern everyone who holds or builds in crypto: the attackers are improving faster than the defenses. The success rate of violent crypto theft attempts has actually fallen — from 67 percent in 2024 to 49 percent in 2025 to 26 percent in 2026 — suggesting that holders are getting smarter about physical security. But the raw number of attacks keeps climbing, and the dollar amounts keep growing, because the pool of targets is larger and the organizational sophistication of attacker groups is higher.

On the protocol side, $1 billion in losses across five months is not a temporary anomaly. It is the market’s verdict on a DeFi ecosystem that has prioritized innovation and liquidity over defense-in-depth security practices. The Term Labs attacker started with $4,800 and walked away with $8.5 million. The KelpDAO attacker walked away with $292 million by compromising infrastructure most users did not know existed. And Lazarus Group, working on behalf of a government that needs hard currency to fund ballistic missile development, has reportedly walked away with more than three-quarters of everything stolen in 2026.

The crypto market this August has generated extraordinary returns for long-term holders. Bitcoin near $80,000, Ethereum up sharply, and a wave of optimism about what regulatory clarity might unlock. None of that changes the fact that the security environment in which those gains exist is the most dangerous it has ever been — not despite the bull market, but in part because of it. Rising prices mean rising stakes, and rising stakes attract more sophisticated attackers.

Nobody cracked the code at Term Labs on August 23. They cracked the system. That distinction — between breaking a contract and breaking the structure around it — is the one that the crypto community needs to internalize, quickly, before the next $8.5 million becomes the next $285 million.


Sources

Bitcoin’s Best August Since 2017: What $79,000 Tells Us About Where This Rally Goes Next

August is supposed to be crypto’s dead season. For the better part of the last five years, the month has delivered nothing but sideways drift, trader frustration, and the particular kind of boredom that convinces retail investors to quietly close their positions and wait for autumn. Bitcoin had not posted a positive August since 2021. The pattern was so reliable it had become a standing joke: survive August, and maybe September would bring something worth watching.

Nobody is laughing now. As of August 27, 2026, Bitcoin is trading at $79,027 — up roughly 25% for the month, on track for its best August performance since 2017, the year it climbed 65% in a single calendar month before igniting one of the most extraordinary bull runs in financial history. Ethereum has reached $2,506. Solana is at $102.17, up nearly 6% on the day alone. The total crypto market capitalization approached $2.7 trillion before easing slightly on an inflation data print. Something has clearly changed — and understanding what changed, and why, matters far more than the price itself.


From Flat to $80,000: What Happened in Ten Days

The move was fast and it was concentrated. Between August 17 and August 21, Bitcoin surged from approximately $60,000 to a brief intraday high above $81,000 — a gain of more than 23% in five trading sessions. Ethereum moved even harder, posting a 29% weekly gain that took it back above $2,500 for the first time since spring. In the same window, Solana added more than 20%, and the broader altcoin market followed with varying degrees of enthusiasm.

The catalyst was not a technical breakout, a protocol upgrade, or a surprise earnings report. It was a room full of people in Washington, D.C.

On August 19, executives from Coinbase, Ripple, Gemini, Robinhood, and several other major platforms met with senior figures in the White House to discuss the trajectory of U.S. digital asset regulation. The conversation had been anticipated for weeks, but what emerged was more significant than most expected. President Trump, during or shortly after the meeting, floated the idea of the United States government establishing a Strategic Bitcoin Reserve — effectively, a proposal for the federal government to become one of the world’s largest Bitcoin holders by design.

That single signal — speculative, unlegislated, and still far from guaranteed — was enough to unlock the market. Within 48 hours, over $1.4 billion in bearish positions had been liquidated as short sellers were forced to cover into a rising price. The feedback loop between rising price, forced short covering, and renewed institutional confidence pushed Bitcoin through level after level that had acted as resistance for months.


This Was Not a Retail Rally

Here is the detail that makes this move structurally different from the short-covering spikes of late 2024 and early 2025: retail investors were not driving it. On-chain data from the period of the rally showed a clear and consistent pattern — large addresses, often associated with institutional custodians and long-term holders, were accumulating aggressively, while smaller address bands were distributing. Coins were flowing from tired hands to better-capitalized ones.

The institutional fingerprints were visible in the ETF data as well. U.S. spot Bitcoin ETFs recorded $1.92 billion in net inflows for the week ending August 21 — the strongest weekly figure since October 2025, when Bitcoin was trading near its cycle high of approximately $126,000. BlackRock’s IBIT was the dominant vehicle on multiple days, with Fidelity’s FBTC running a close second. Spot Ether ETFs added approximately $697 million in the same period.

Market intelligence firm Wintermute noted that hedge funds and asset managers now account for a larger share of over-the-counter spot volume than in any prior cycle, a shift that reflects the maturing institutional infrastructure that has built up around crypto since the ETF approvals of 2024. This is no longer a market driven primarily by retail speculation on offshore exchanges. The money moving prices today is coming from the same institutions that move prices in equities, bonds, and commodities.


Strategy’s Turning Point — and What It Means for Supply

One of the most closely watched side-stories of the rally involves Strategy, the business intelligence firm formerly known as MicroStrategy that transformed itself into a Bitcoin holding company. Strategy currently holds approximately 840,447 BTC, acquired at an average cost basis of around $75,400 per coin.

When Bitcoin crossed $75,000 during the August surge, Strategy’s holdings shifted from a notional loss of approximately $10 billion to a gain of roughly $1.4 billion — an extraordinary turnaround in a matter of days. Analysts noted that a company back in the black on its core asset class has both the financial capacity and the incentive to resume accumulation. While Strategy did not add to its holdings during the August breakout, the expectation that it may do so in coming weeks represents a meaningful supply pressure dynamic for the market to absorb.


Today’s Inflation Speed Bump

August 27 brought the first test of the rally’s resilience. The U.S. Personal Consumption Expenditures (PCE) index — the Federal Reserve’s preferred inflation gauge — came in at 3.7% annually, a tenth of a percentage point hotter than economists had forecast. The reading triggered an immediate intraday dip across crypto markets, as investors recalibrated expectations for Federal Reserve interest rate cuts later in the year.

The dip did not hold. Bitcoin recovered to $79,027 by mid-session, Ethereum climbed 2.58%, and Solana continued its outperformance with a gain approaching 6%. The speed of the recovery suggests that the market’s underlying bid — the institutional buyers who drove the original rally — remains present and willing to absorb selling pressure triggered by macro noise.

That said, the inflation print is a reminder that crypto does not operate in a vacuum. A Federal Reserve that feels compelled to keep rates higher for longer, or worse, to resume tightening, would represent a meaningful headwind for risk assets across the board. Rate-sensitive markets have had a complicated relationship with crypto since 2022, and any deterioration in the macro environment would test whether institutional conviction is as durable as the August performance suggests.


Context: Where We Actually Are

For all the excitement of August, some perspective is essential. Bitcoin’s 52-week range runs from $57,945 to $126,080. The upper bound of that range — the cycle high hit in October 2025 — sits approximately 33% above where Bitcoin trades today. The August rally, impressive as it is, represents recovery from a multi-month correction, not the opening act of a new all-time high campaign.

The broader altcoin picture is similarly mixed. XRP is actually down slightly on the day at $1.42, and many mid-cap tokens remain significantly below their 2025 peaks. The market is not in indiscriminate bull mode — it is in a selective, institutionally led recovery that has benefited Bitcoin and Ethereum most directly, with spillover to high-liquidity layer-1 networks like Solana.

What has changed is the analyst consensus around where Bitcoin goes from here. A growing number of research desks are now projecting a return to $100,000 before the end of 2026 — a target that seemed remote in June and ambitious in July but now appears within reach given the right macro conditions and continued institutional inflows.


What This Means for You

If you have been watching from the sidelines, the natural impulse right now is to chase. Resist it. Markets that move 25% in a month tend to consolidate before moving higher, and the PCE inflation data released today is exactly the kind of trigger that can compress prices quickly before the next leg. Patience in entry, particularly for those considering meaningful position sizing, has historically been rewarded in crypto’s recovery cycles.

If you are already positioned, August has done you a favour — but it has also likely changed your portfolio’s risk profile. A position that was 10% of your portfolio in July may now be 12.5%, and the discipline of rebalancing is easy to ignore when markets are moving in your favour. Consider your original allocation targets and whether the current weighting still reflects your actual risk tolerance.

For those focused on the longer arc: the institutional infrastructure that drove this rally — spot ETFs, regulated custody, OTC desks serving hedge funds and asset managers — is not going away. It represents a structural change in how capital accesses Bitcoin. Whether the Strategic Bitcoin Reserve ever becomes policy is almost beside the point; the signal it sent about the direction of U.S. political sentiment toward crypto was clear enough to move billions. That kind of policy tailwind, once established, tends to be durable.


August 2017 ended with Bitcoin at roughly $4,700. The year closed above $19,000. Nobody is drawing that comparison casually — the market structure is entirely different, the participant base is far larger, and the leverage dynamics have changed. But the historical rhyme is striking: a month that defied its own seasonal pattern, powered by a structural shift in who was buying and why, followed by an analyst consensus that the cycle still had room to run.

We are 33% below the last high. The institutions are here. The policy wind is shifting. The dead season is over.


Sources:

The Machine Economy Arrives: How AI Agents Became Blockchain’s Most Powerful Users

By March of this year, artificial intelligence agents had initiated more than 15 million transactions on the Solana blockchain alone. Not humans clicking buttons on a trading interface. Not bots running simple arbitrage loops. Fully autonomous AI systems — carrying their own wallets, managing their own funds, and negotiating directly with other machines — had quietly become one of the most active classes of participants in the entire crypto ecosystem. The machine economy, long promised and long derided, had simply arrived while most people were looking somewhere else.

That figure, drawn from on-chain data tracking AI agent activity through Q1 2026, represents something larger than a usage statistic. It marks an inflection point in the relationship between artificial intelligence and blockchain infrastructure — a convergence that is now reshaping everything from how GPU computing is priced to what “payment rails” actually means in a world where the payer is not a person.

The Numbers That Rewrote the Narrative

For most of 2024 and into early 2025, AI-themed crypto tokens were largely a speculative sideshow — projects with compelling whitepapers and eye-catching names that rose and fell with the broader market cycle. The AI-agent crypto sector as a whole was frequently dismissed as narrative-chasing. That characterization is now difficult to defend.

By Q1 2026, the combined market capitalization of AI agent crypto projects had climbed to approximately $15.3 billion. Virtuals Protocol alone commanded a valuation above $5 billion after enabling roughly 14,000 AI agent tokens on its platform. ai16z — the open-source project built around the Eliza agent framework — reached a market cap of $1.63 billion. Bittensor, the decentralized AI network that organizes intelligence into specialized “subnets,” was valued between $3.2 and $3.4 billion. These are not trivial numbers for projects that did not exist five years ago.

More revealing than market caps, though, is transaction volume. The x402 protocol — Coinbase’s system for embedding stablecoin payments directly into HTTP requests, allowing AI agents to pay for API access the way a browser loads a webpage — recorded nearly 500,000 payments in a single week at its peak this year. Stripe launched its own machine payments layer on Base in February 2026. MoonPay followed with a non-custodial agent payment infrastructure supporting eight blockchain networks. Payment infrastructure for autonomous AI, once theoretical, has become a genuine commercial sector.

Decentralized Compute: The GPU Shortage That Built an Industry

To understand why AI agents are converging on blockchain infrastructure specifically, you have to understand where they need to run. AI systems require enormous amounts of GPU compute — and that compute has been, for several years now, controlled by a very small number of organizations.

NVIDIA H100 and H200 chips faced lead times of six months or more through much of 2024. Amazon Web Services, Microsoft Azure, and Google Cloud collectively control approximately 65 percent of available GPU capacity worldwide. An AI startup or autonomous agent that wants to run inference workloads at scale has essentially been at the mercy of three hyperscalers and their pricing structures. AWS charges $32.77 per hour for a cluster of eight A100 GPUs. That is the reference price against which everything in decentralized compute is being measured.

A cluster of networks built on blockchain rails is now offering a credible alternative. io.net, which aggregates idle GPU capacity from data centers, crypto miners, and individual device owners into rentable clusters, has grown its monthly active addresses from 8,000 in Q1 2025 to 45,000 in Q1 2026 — nearly a fivefold increase in twelve months. The network claims access to over 100,000 GPU devices and prices equivalent compute at $12 to $28 per hour, representing discounts of 15 to 63 percent against hyperscaler rates. For certain workloads, particularly batch inference, the savings can reach 60 to 90 percent.

Akash Network (AKT) has carved a different niche, running GPU compute auctions where prices settle at 80 to 90 percent below AWS pricing for uncensored LLM workloads — tasks that the major cloud providers have become increasingly reluctant to host. Render Network (RNDR), with a market cap above $1.5 billion, focuses on GPU rendering but has expanded into AI inference. Together, these projects managed an estimated $180 to $220 million in annualized protocol revenue as of Q1 2026 — real commercial activity, not just token speculation.

Gensyn, the AI compute startup backed by Andreessen Horowitz’s a16z with a $43 million Series A, is building verification infrastructure that allows distributed GPU networks to prove that they actually ran the computations they claimed to run — a problem that has historically made decentralized compute less trustworthy than centralized alternatives. If Gensyn’s approach works at scale, it removes one of the last serious objections to replacing hyperscaler infrastructure with blockchain-coordinated compute.

The Payment Rails Powering Machine-to-Machine Commerce

Traditional payment infrastructure was designed for humans. It assumes that the entity initiating a transaction can wait for bank settlement windows, can navigate KYC requirements, can log into a web interface and click a confirmation button. None of those assumptions hold for an AI agent running 24 hours a day, making thousands of micro-decisions, and needing to pay for API access in real time.

Blockchain solves this problem structurally. A smart contract wallet with a stablecoin balance can authorize payments programmatically, settle in seconds, and operate across borders without a correspondent banking relationship. This is not a theoretical advantage — it is the reason AI agents are defaulting to on-chain payment infrastructure even when off-chain alternatives exist.

The x402 protocol, launched by Coinbase, embeds HTTP 402 (“Payment Required”) responses with on-chain settlement instructions. An AI agent browsing the web for data or API access receives a 402 response, pays in USDC on Base, and proceeds — the entire transaction completing in under a second. The protocol processed nearly half a million payments in its peak week in early 2026. Stripe’s machine payments layer on Base offers a parallel infrastructure for the e-commerce and enterprise ecosystem. MoonPay’s agent layer extends the model across eight blockchain networks for maximum routing flexibility.

Illia Polosukhin, co-founder of NEAR Protocol — which launched a “super app” at the crypto-AI intersection in February 2026 — put it plainly: “In a few years, it’s going to be just AI, like the operating system.” NEAR’s thesis is that blockchain becomes the default settlement layer for an AI-native internet, the same way TCP/IP became the default communication layer for the human internet. The payment infrastructure taking shape in 2026 looks consistent with that prediction.

The Infrastructure Stack Taking Shape

What is emerging is not a single protocol but a layered stack — compute at the bottom, intelligence in the middle, and agent-facing applications at the top.

At the compute layer, DePIN (Decentralized Physical Infrastructure Networks) projects like io.net, Render, and Akash provide raw GPU resources. At the intelligence layer, Bittensor’s 100-plus specialized subnets allow developers to fine-tune models for specific tasks — everything from protein folding to financial prediction — while the Superintelligence Alliance, formed from the merger of Fetch.ai, SingularityNET, and Ocean Protocol, is building shared infrastructure for open AI development. At the application layer, Virtuals Protocol enables the creation and monetization of AI agent personas, while Uniswap shipped seven open-source AI Skills in February 2026 to let agents interact with decentralized finance protocols directly.

Solana has emerged as a preferred settlement layer for much of this activity. Its capacity to process 65,000-plus transactions per second and its near-zero transaction costs make it practical for the high-frequency, low-value payments that AI agent commerce generates. io.net settled its reward layer on Solana specifically because it reduces settlement costs by an estimated 99 percent versus Ethereum. The network effects are compounding: as more AI projects choose Solana for settlement, it becomes the obvious default for the next project, which brings more liquidity, which attracts more builders.

Forecasters are beginning to assign large numbers to where this leads. McKinsey projects agentic commerce — economic activity initiated and completed by AI agents — could reach $3 to $5 trillion globally by 2030. The agentic payment market specifically is forecast to grow from $7 billion today to $93 billion by 2032. Capgemini estimates the enterprise AI agents market at $47 billion by 2030, growing at a 44 percent compound annual rate. Even applying a steep discount to projections of this kind, the direction is clear.

What This Means for You

If you hold crypto assets or participate in DeFi, the rise of AI agents as primary blockchain users changes the environment you are operating in. Here is how:

  • Liquidity patterns are shifting. AI agents already account for more than 30 percent of trading volume on Polymarket, the prediction market platform. On decentralized exchanges, agent-driven trading strategies execute continuously and react to price movements faster than any human trader. This changes how price discovery works and increases both liquidity and volatility in certain markets.
  • New investment categories have emerged. DePIN compute projects, agentic payment protocols, and AI agent platforms are now distinct asset categories with their own valuation metrics — compute utilization rates, inference cost comparisons, and GitHub commit activity rather than just TVL or trading volume. Understanding these metrics matters if you are evaluating tokens in this space.
  • Infrastructure is the moat. The projects building the plumbing — the GPU networks, the settlement layers, the payment protocols — are likely to capture durable value regardless of which AI agent applications become popular. io.net, Render, Bittensor, and Akash are infrastructure plays, not AI agent bets. The distinction matters.
  • Security considerations are new. AI agents operating autonomously with real funds introduce novel attack vectors. Projects like the Forta network and Cyfrin provide real-time exploit detection for agent activity, but the security landscape for autonomous on-chain agents is still maturing. Interacting with AI agent protocols carries risk profiles that are genuinely different from interacting with conventional DeFi.

The Infrastructure Moment

Fifteen million AI agent transactions on a single blockchain in a single quarter. Half a million autonomous payments in a single week. A decentralized GPU market growing at nearly five times its 2025 pace. These numbers describe a convergence that is already well underway — not something that analysts are projecting for some future cycle.

The earliest days of the internet looked something like this: the infrastructure was taking shape, the commercial applications were still rough, the valuations were volatile, and it was genuinely unclear which specific companies would survive. What was not unclear was the direction. AI and blockchain are building the transaction layer for a world where machines are economic actors in their own right. The 15 million transactions counted through March were just the first sentence of that story.


Sources:
Yellow.com Research: AI Compute Demand and Crypto GPU Networks Gap 2026
Geek Metaverse: How AI Agents Are Becoming the Primary Users of Blockchain in 2026
CoinIdol: The Convergence of AI and Real-World Assets Dominates August 2026 Crypto Narratives
KuCoin: The Great Convergence — 2026 Strategic Deep-Dive into the AI + Crypto Landscape
KuCoin: AI Compute + Crypto — The Next $10B Narrative?

The SEC Just Rewrote the Crypto Rulebook: Inside the $75 Million Framework Changing How Tokens Raise Capital

On the morning of August 18, 2026, the U.S. Securities and Exchange Commission did something it hadn’t done in the thirty-year history of digital assets: it proposed rules written specifically for crypto.

Not adapted from rules written for stocks. Not stretched to fit tokens through years of enforcement actions and no-action letters. Rules built from scratch, with blockchain in mind, under a name that leaves no ambiguity about what they cover: Regulation Crypto Assets.

The proposal, championed by SEC Chairman Paul S. Atkins, opens two fundraising exemptions, creates a novel safe harbor that lets token projects graduate out of securities law entirely, and wipes away the state-by-state compliance patchwork that has choked crypto capital formation for years. It is, in the words of Atkins himself, a framework designed to give “crypto asset entrepreneurs and market participants with clear pathways to raise capital” — and to reduce the pressure on American projects to move offshore to do it.

If it becomes law, it will reshape how crypto projects are born, funded, and eventually set free. Here is what you need to know.


The Problem the SEC Is Finally Trying to Solve

For the better part of a decade, crypto companies operating in the United States have navigated securities law through a combination of guesswork, expensive legal opinions, and fear. The SEC’s longstanding position — that most token offerings constitute investment contracts and therefore require full registration, or an exemption, under the Securities Act of 1933 — was never written into clear rules. It was enforced through lawsuits.

The cost of that ambiguity was enormous. Projects that wanted to sell tokens to U.S. investors faced the same disclosure and registration burden as a company listing on the NYSE, a process designed for entities with auditors, legal departments, and years of financial history. Most early-stage crypto teams have none of those things. So they either raised exclusively from accredited investors in private placements, excluded American users from token sales entirely, or moved their legal domicile to Switzerland, the Cayman Islands, or Singapore — and raised money abroad while hoping the SEC wouldn’t follow.

Regulation Crypto Assets is the SEC’s acknowledgment that this system wasn’t working — not for entrepreneurs, not for investors, and arguably not for the United States.


The Startup Exemption: A $5 Million On-Ramp

The first of the two new fundraising pathways is built for early-stage projects. Under the proposed startup exemption, an issuer — whether an individual, a company, or even a non-U.S. entity — can raise up to $5 million over a four-year period without audited financial statements, without SEC staff review, and without the full weight of registration requirements.

Instead, issuers would file a simplified form called Form NOR and provide what the SEC describes as “principles-based narrative disclosures” to prospective investors: plain-language explanations of what the project is, how the funds will be used, what the token does, and what risks investors face. The exemption also covers airdrops, staking rewards, and governance token distributions — acknowledging that crypto projects often distribute tokens in ways that have no analog in traditional finance.

There is one significant constraint: the exemption is one-time use per issuer and per crypto asset. A project cannot repeatedly tap this pathway as it grows. Once used, the startup exemption is spent. Teams that need more capital will have to move up to the second tier — or pursue traditional registration.


The Fundraising Exemption: Up to $75 Million per Year

For projects that have outgrown the startup phase but still aren’t ready for full public registration, Regulation Crypto Assets proposes a two-tier fundraising exemption modeled loosely on the existing Regulation A framework for conventional securities.

Tier 1 allows issuers to raise up to $20 million in any 12-month period. Tier 2 raises that ceiling to $75 million per year. Both tiers require U.S. entity status for the issuer and SEC staff review and qualification through a new form called Form 1-CRYPTO. Tier 2 also imposes ongoing reporting obligations — annual, semiannual, and current reports — and caps the amount that non-accredited investors can contribute to 10 percent of their income or net worth, a guardrail designed to prevent retail investors from concentrating too much of their savings in high-risk token offerings.

The practical effect is a graduated on-ramp into the American capital markets. A small team building a new Layer 2 protocol could raise seed capital under the startup exemption, scale to a Series A-equivalent under Tier 1, and reach a much larger investor base under Tier 2 — all within a framework purpose-built for how crypto projects actually develop, not how steel companies issue bonds.


The Safe Harbor: The Most Consequential Piece

The startup and fundraising exemptions are significant. But the most consequential element of Regulation Crypto Assets may be the investment contract safe harbor — because it creates a mechanism for a token to stop being a security altogether.

Under the proposal, a crypto asset can exit securities regulation entirely once an issuer has completed all of the “essential managerial efforts” it promised to investors when the token was first offered. In other words: once the project is built, the network is running, and the team’s work is done, the token can file a transition report on Form TR and emerge from under the SEC’s jurisdiction.

This matters enormously. One of the central frustrations of the crypto industry has been that tokens sold as securities — under the theory that investors were counting on the founding team to build something valuable — could theoretically remain securities forever, even after the project was fully decentralized and the founding team had moved on. The safe harbor puts a defined end point on that classification. Build the thing. Complete the work. File the form. Move on.

The safe harbor is available to any issuer that meets the conditions, regardless of which exemption it used during fundraising — or even to projects that raised under existing exemptions before Regulation Crypto Assets existed.


The CLARITY Act Backdrop: Why Congress Still Matters

Regulation Crypto Assets does not exist in a vacuum. It was proposed by an SEC explicitly designed to complement the Digital Asset Market Clarity Act — the comprehensive crypto market structure bill, known as the CLARITY Act, that has been working its way through Congress since 2025.

The CLARITY Act passed the House of Representatives with a strong bipartisan vote of 294 to 134 in July 2025, and advanced out of the Senate Banking Committee in May 2026 by a 15-9 margin. It proposes a fundamental reorganization of crypto oversight: tokens whose value derives primarily from functioning blockchains would be classified as “digital commodities” and regulated by the CFTC rather than the SEC. Projects could earn a “mature blockchain” certification that triggers the regulatory handoff. Non-custodial software developers would be shielded from money-transmitter requirements that have threatened open-source protocol builders.

But in the Senate, the bill hit a wall. Senate Majority Leader John Thune confirmed the bill would not reach the floor before the August recess. The math is daunting: Republicans hold 53 seats, but cloture — the procedural vote to end debate — requires 60. Only two Democrats, Senators Ruben Gallego and Angela Alsobrooks, have signaled support, leaving the bill several votes short. Prediction markets tracked the collapse in real time: Polymarket’s odds of 2026 passage fell from 82 percent in February to just 28 percent by July 30.

The remaining disputes are not trivial. Democrats want stronger ethics language preventing elected officials from issuing digital assets; the current Senate Republican draft includes a prohibition that sunsets on January 20, 2029, and is not retroactive. DeFi developer liability and stablecoin yield restrictions on exchanges remain unresolved. September’s packed legislative calendar — appropriations battles, midterm positioning — offers little room for a contentious crypto bill to find floor time.

The SEC’s proposal can be read, in part, as a hedge against Congressional inaction. It gives industry something concrete to work with today, independent of whether the CLARITY Act ever passes.


What This Means for You

If you are a crypto founder or developer, Regulation Crypto Assets is the most consequential regulatory development in years — but it is still a proposal, not a law. The 60-day public comment period that began after the Federal Register publication is the industry’s opportunity to shape the final rules. Teams with an interest in the exemption thresholds, the disclosure requirements, or the safe harbor conditions should engage now, either directly or through industry associations. Final rules are likely several months away at the earliest.

If you are an investor, the proposal signals a meaningful shift in regulatory posture. A framework that lowers the cost of legal compliance for U.S.-based token projects may bring more high-quality projects back onshore — and give retail investors access to opportunities that were previously restricted to accredited investors or simply unavailable in the United States. More supply, with clearer legal standing, tends to be good for market health.

If you are watching Washington, the divergence between SEC action and Congressional stalemate is the defining dynamic right now. The SEC can propose rules; only Congress can create the legislative certainty the industry ultimately needs. The CLARITY Act’s fate in September and October — whether Senate leadership finds the floor time, whether Democrats and Republicans can bridge the ethics and DeFi disputes — will determine whether Regulation Crypto Assets becomes a permanent framework or a placeholder for something more comprehensive.

For the first time in a long time, the federal government is writing rules for crypto rather than enforcing rules written for something else. That is progress, whatever comes next.


Sources:

$1.1 Billion and Counting: How Lazarus Group Is Dismantling Crypto Security in 2026

You did everything right. You used a hardware wallet. You never clicked a suspicious link. You kept your seed phrase offline, written in two different locations, never photographed. And then, one morning in April 2026, $285 million in cryptocurrency belonging to users just like you — protected by protocols just like those — vanished in under an hour. Not because a smart contract had a bug. Not because an exchange got hacked. Because a software developer at a DeFi protocol answered what looked like a LinkedIn message from a recruiter at a prestigious firm.

That is the new reality of crypto security in 2026. The attack surface has shifted from code to people, from on-chain logic to off-chain trust, and the group driving that shift is operating at a scale that has no precedent in the history of financial crime.


The Numbers That Define a Crisis

The statistics from the first half of 2026 are difficult to absorb. Three independent security firms — Immunefi, Quill Audits, and TRM Labs — each using different methodologies, converged on the same conclusion: 212 verified exploits generated more than $1.1 billion in losses in the first six months of the year. That represents 3.4 times the incident count of all of 2025 combined, not six months of it — all of it.

DefiLlama tracked more than 140 exploits by mid-year that collectively exceeded $1 billion stolen. Immunefi put DeFi-specific losses at $680.3 million for the first half alone. The Q2 record stands at 99 separate incidents — more exploits in a single quarter than many analysts had projected for the entire year.

Perhaps the most sobering number of all: only 6.5 percent of stolen funds were recovered in Q1 2026. For every $100 taken, about $93.50 is gone permanently. For the victims of the two largest attacks of the year, the math is even starker. Neither Drift Protocol’s $285 million nor KelpDAO’s $292 million has been substantially recovered. Together, those two incidents account for roughly half of all H1 losses — and neither of them exploited a single line of faulty smart contract code.


How Lazarus Group Changed the Rules

North Korea’s Lazarus Group — operating under the Reconnaissance General Bureau, the country’s primary intelligence directorate — is attributed by multiple blockchain intelligence firms with approximately 55 percent of all H1 2026 losses, roughly $609 million in six months. Across all known operations since the group began targeting cryptocurrency markets, cumulative theft now exceeds $6.75 billion.

The UN Panel of Experts has documented in successive annual reports how proceeds from these thefts fund Pyongyang’s weapons development programs. Chainalysis and OFAC — which placed Lazarus on its Specially Designated Nationals list in April 2022 — have both traced laundered funds through a predictable four-stage sequence: rapid cross-chain movement within hours of a theft, mixing through services outside U.S. jurisdiction, chain-hopping across Ethereum, Avalanche, BNB Chain, and Bitcoin, and final fiat conversion through over-the-counter desks in Southeast Asia and the Middle East.

What has changed in 2026 is not the group’s ambition — it is their methodology. The two largest thefts of the year required no vulnerability in any blockchain protocol whatsoever. “Neither attack required finding a vulnerability in any smart contract,” TRM Labs noted in their mid-year security report. Instead, Lazarus shifted its energy to the weakest layer of any decentralized system: the human beings who run it.


The $577 Million Bridge Problem

Before examining the human angle, it is worth understanding the technical vector that enabled the KelpDAO breach — because it illustrates a structural vulnerability affecting billions of dollars in assets right now.

Cross-chain bridges — the infrastructure that allows assets to move between different blockchains — hold an estimated $21.94 billion in total value locked as of mid-2026. They have also accounted for roughly 40 percent of all value ever hacked in Web3 since 2022. In 2026 alone, bridge exploits across eight separate incidents totaled $328.6 million.

The KelpDAO attack on April 19 stands as the year’s largest single incident at $292 million. Attackers drained 116,500 rsETH — approximately 18 percent of the token’s circulating supply — by spoofing a cross-chain message through LayerZero’s messaging layer. The exploit tricked the bridge into believing a valid instruction had arrived from another network. Because the emergency multisig pause took 46 minutes to activate, the funds were long gone. The collateral damage rippled across more than 20 connected blockchains simultaneously.

The core vulnerability was architectural: when bridge verifier configurations rely on a single point of failure, an attacker who can spoof one valid message can drain the entire liquidity pool. The June cross-chain bridge exploit that drained $127 million from three protocols in twelve minutes used the same signature-replay method — valid signatures reused across chains due to missing chain-specific nonces — suggesting the lesson had not been universally applied.


When Your Team Is the Vulnerability

The Drift Protocol breach tells a different story — and a more personally unsettling one for anyone who works in or around crypto.

According to threat intelligence firm Mandiant and corroborated by Phemex’s incident analysis, a North Korean hacking unit designated UNC4736 conducted a six-month social engineering campaign targeting Drift Protocol team members before the April 1 theft. The initial approach was a fake recruiter message on a professional networking platform. Over weeks, the attacker built rapport, eventually persuading a developer to download what was presented as a coding assessment. The file contained malware that extracted administrative keys from the target’s machine.

With those keys, the attackers accessed the protocol’s multisig infrastructure. No smart contract vulnerability required. Lazarus Group’s operatives conduct months of open-source intelligence gathering before making first contact, building personas that are difficult to distinguish from legitimate recruiters at firms the target would recognise. The industry produced excellent tooling for auditing Solidity code. It produced far less for training team members to recognise a convincing fake LinkedIn recruiter.


AI Agents: The Attack Surface Nobody Planned For

In May 2026, the first documented exploit of a cryptocurrency AI agent occurred, targeting a platform called Bankr. The theft was approximately $175,000 — relatively small — but the method was a preview of a much larger problem.

The attacker encoded malicious financial instructions in Morse code within a transaction payload. Bankr’s AI agent, which held authority to execute trades autonomously, processed the message as legitimate financial authorization because its safety filters were not designed to interpret Morse-encoded instructions. The agent executed a series of unauthorized transfers before the exploit was identified.

Blockchain security firm Blockaid estimates that AI agent deployments in crypto are growing at roughly ten times annually. Each new agent represents a novel attack surface: a system that can hold funds, execute transactions, and make decisions — often faster than any human can intervene — but whose decision-making logic can be manipulated through inputs its designers did not anticipate. The exploit taxonomy for AI agents is still being written in real time, and the industry is deploying them faster than it is securing them.


What This Means for You

If you are a retail crypto holder, the most actionable takeaways from the 2026 security landscape concern bridge exposure and protocol due diligence. Before depositing funds into any DeFi protocol that relies on cross-chain bridging, check whether that bridge has undergone independent security audits specifically addressing its verifier architecture and replay-attack protections. Several DeFi dashboards now display audit histories; look for audits conducted within the past twelve months, since architectures change.

If you work at a crypto company in any role — developer, operations, marketing, finance — treat unsolicited professional outreach with a level of caution that would have seemed paranoid two years ago. Legitimate recruiters do not ask candidates to download executables as part of an application process. If a pre-employment test involves running software on your personal or work machine, verify the recruiting firm directly through independently sourced contact details before proceeding.

For those who interact with AI-powered trading tools or DeFi agents: understand what permissions each agent holds and whether those permissions can be revoked quickly. Treat AI agent authorization the same way a prudent person treats bank signatory authority — the fewest systems possible should hold it, with clear limits and audit trails in place before the first dollar is committed.

Finally, consider recovery expectations soberly. At a 6.5 percent recovery rate, the practical assumption when funds are stolen from a DeFi protocol in 2026 is that they are gone. That makes due diligence before depositing far more valuable than any post-exploit response plan.


The Bigger Picture

There is a useful framing for what is happening in 2026’s crypto security landscape: the industry built extraordinary walls around its code and left the doors to its people wide open. The $1.1 billion taken in the first half of the year was not stolen because blockchain technology failed. It was stolen because human trust relationships, bridge architecture edge cases, and novel AI attack surfaces were not treated with the same engineering rigor as the smart contracts themselves.

The attackers adapted. The question now is whether protocols, security firms, and individual users can do the same before the second half of 2026 writes an even larger number.


Sources: